(SYS.04) — PERSONAL PRODUCT — LOCAL-FIRST MOBILE SECURITY
Vaultify
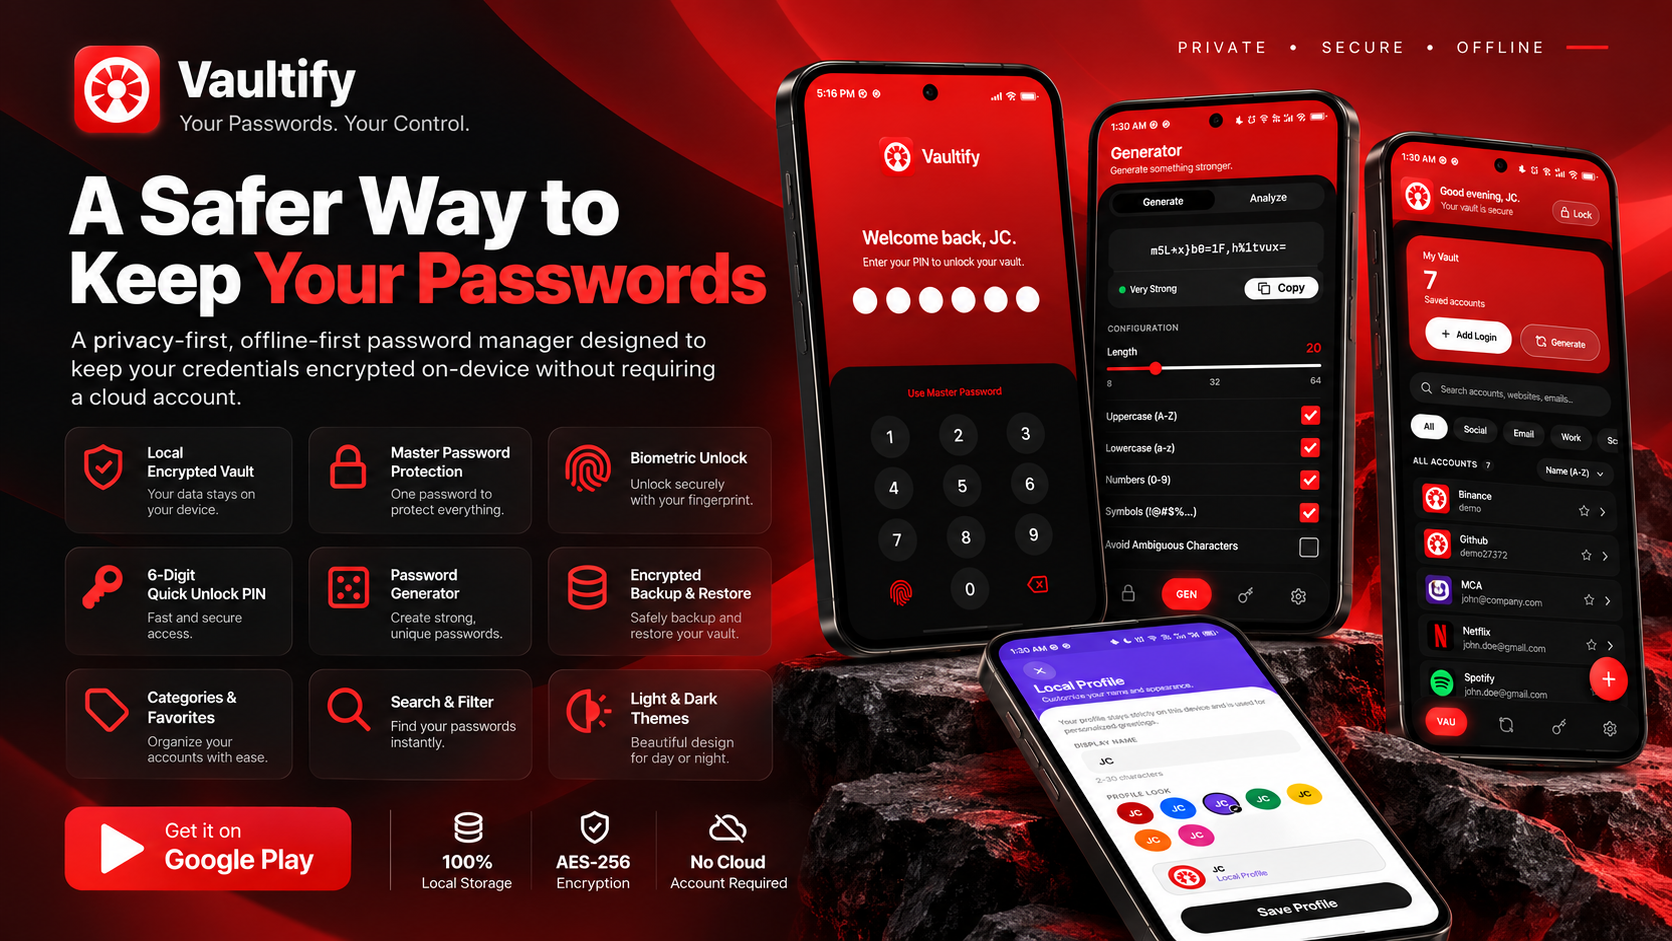
Privacy-first, offline-first password manager with AES-GCM-256 local encryption.
(01) — System Overview
PROJECT
CONTEXT.
A privacy-first, local-first hybrid mobile password manager built with Ionic Vue, TypeScript, and Capacitor. Encrypts sensitive credentials on-device using authenticated AES-GCM-256 and PBKDF2 key derivation, supporting master-password, six-digit quick PIN, and native biometric unlock without requiring a cloud account.
The Operational Bottleneck / Problem
Cloud password managers introduce third-party breach risks, mandatory subscription models, and privacy trade-offs for users who prefer keeping sensitive credentials strictly on their personal hardware.
Engineering Solution
Created a standalone, zero-cloud mobile application that keeps encryption keys and credentials securely contained on-device.
(02) — Architecture & Pipeline
SYSTEM
ARCHITECTURE.
Ionic Vue mobile client executing SubtleCrypto Web Crypto APIs for encryption/decryption, persisting encrypted blobs via Capacitor Preferences, with native platform biometric hooks.
Data & Execution Pipeline
(03) — Technical Focus
ENGINEERING
HIGHLIGHTS.
Local-First Zero-Knowledge Architecture
Vault data is encrypted locally using 256-bit AES-GCM before writing to device storage; core credential functionality operates completely offline without remote accounts or server dependencies.
Multi-Tier Unlock around a Single Vault Key
Engineered a unified vault key architecture that permits unlocking via master password, wrapped six-digit PIN, or native platform biometrics (fingerprint/Face ID) without storing plaintext passwords.
Encrypted Portability & Backups
Developed portable encrypted backup export and restore functionality, requiring the master password for decryption while excluding raw biometric secrets from backup payloads.
Lifecycle-Aware Memory Protection
Implemented automatic vault locking on app backgrounding and inactivity timeouts, purging sensitive decrypted credentials from in-memory state.
(04) — Implemented Capabilities
CORE
FEATURES.
Local authenticated AES-GCM-256 credential encryption
Master password derivation via PBKDF2 + SHA-256 with high iterations
Six-digit quick PIN unlock with attempt-lockout protection
Native platform biometric unlock (Fingerprint / Face ID)
Cryptographically secure password generator with character filters
Password strength analysis powered by zxcvbn-ts
Encrypted JSON backup export and password-authenticated restore
Category organization, favorites tagging, and instant search
Configurable inactivity auto-lock and background purge
Automated Android release builds via GitHub Actions
(05) — Technology Stack
STACK
ARCHITECTURE.
Mobile & UI
Native & Runtime
Cryptography & Security
DevOps & CI/CD
(06) — Problem Solving
TECHNICAL
CHALLENGES.
Balancing Convenience with True Offline Security
Designed an encrypted key-wrapping scheme that allows quick PIN and biometric convenience while ensuring the underlying 256-bit vault key remains cryptographically sealed at all times.
(07) — Reliability & Governance
SECURITY & TESTING.
Privacy & Security Model
Zero cloud databases, zero telemetry tracking, and zero plain credential transmission. Web Crypto API ensures hardware-backed cryptographic execution.
EXPLORE MORE WORK